Track more data with server-side tracking resilient to ad blockers and browser restrictions.
Persistent Cookies & IDs
Recognize your visitors every time they return.
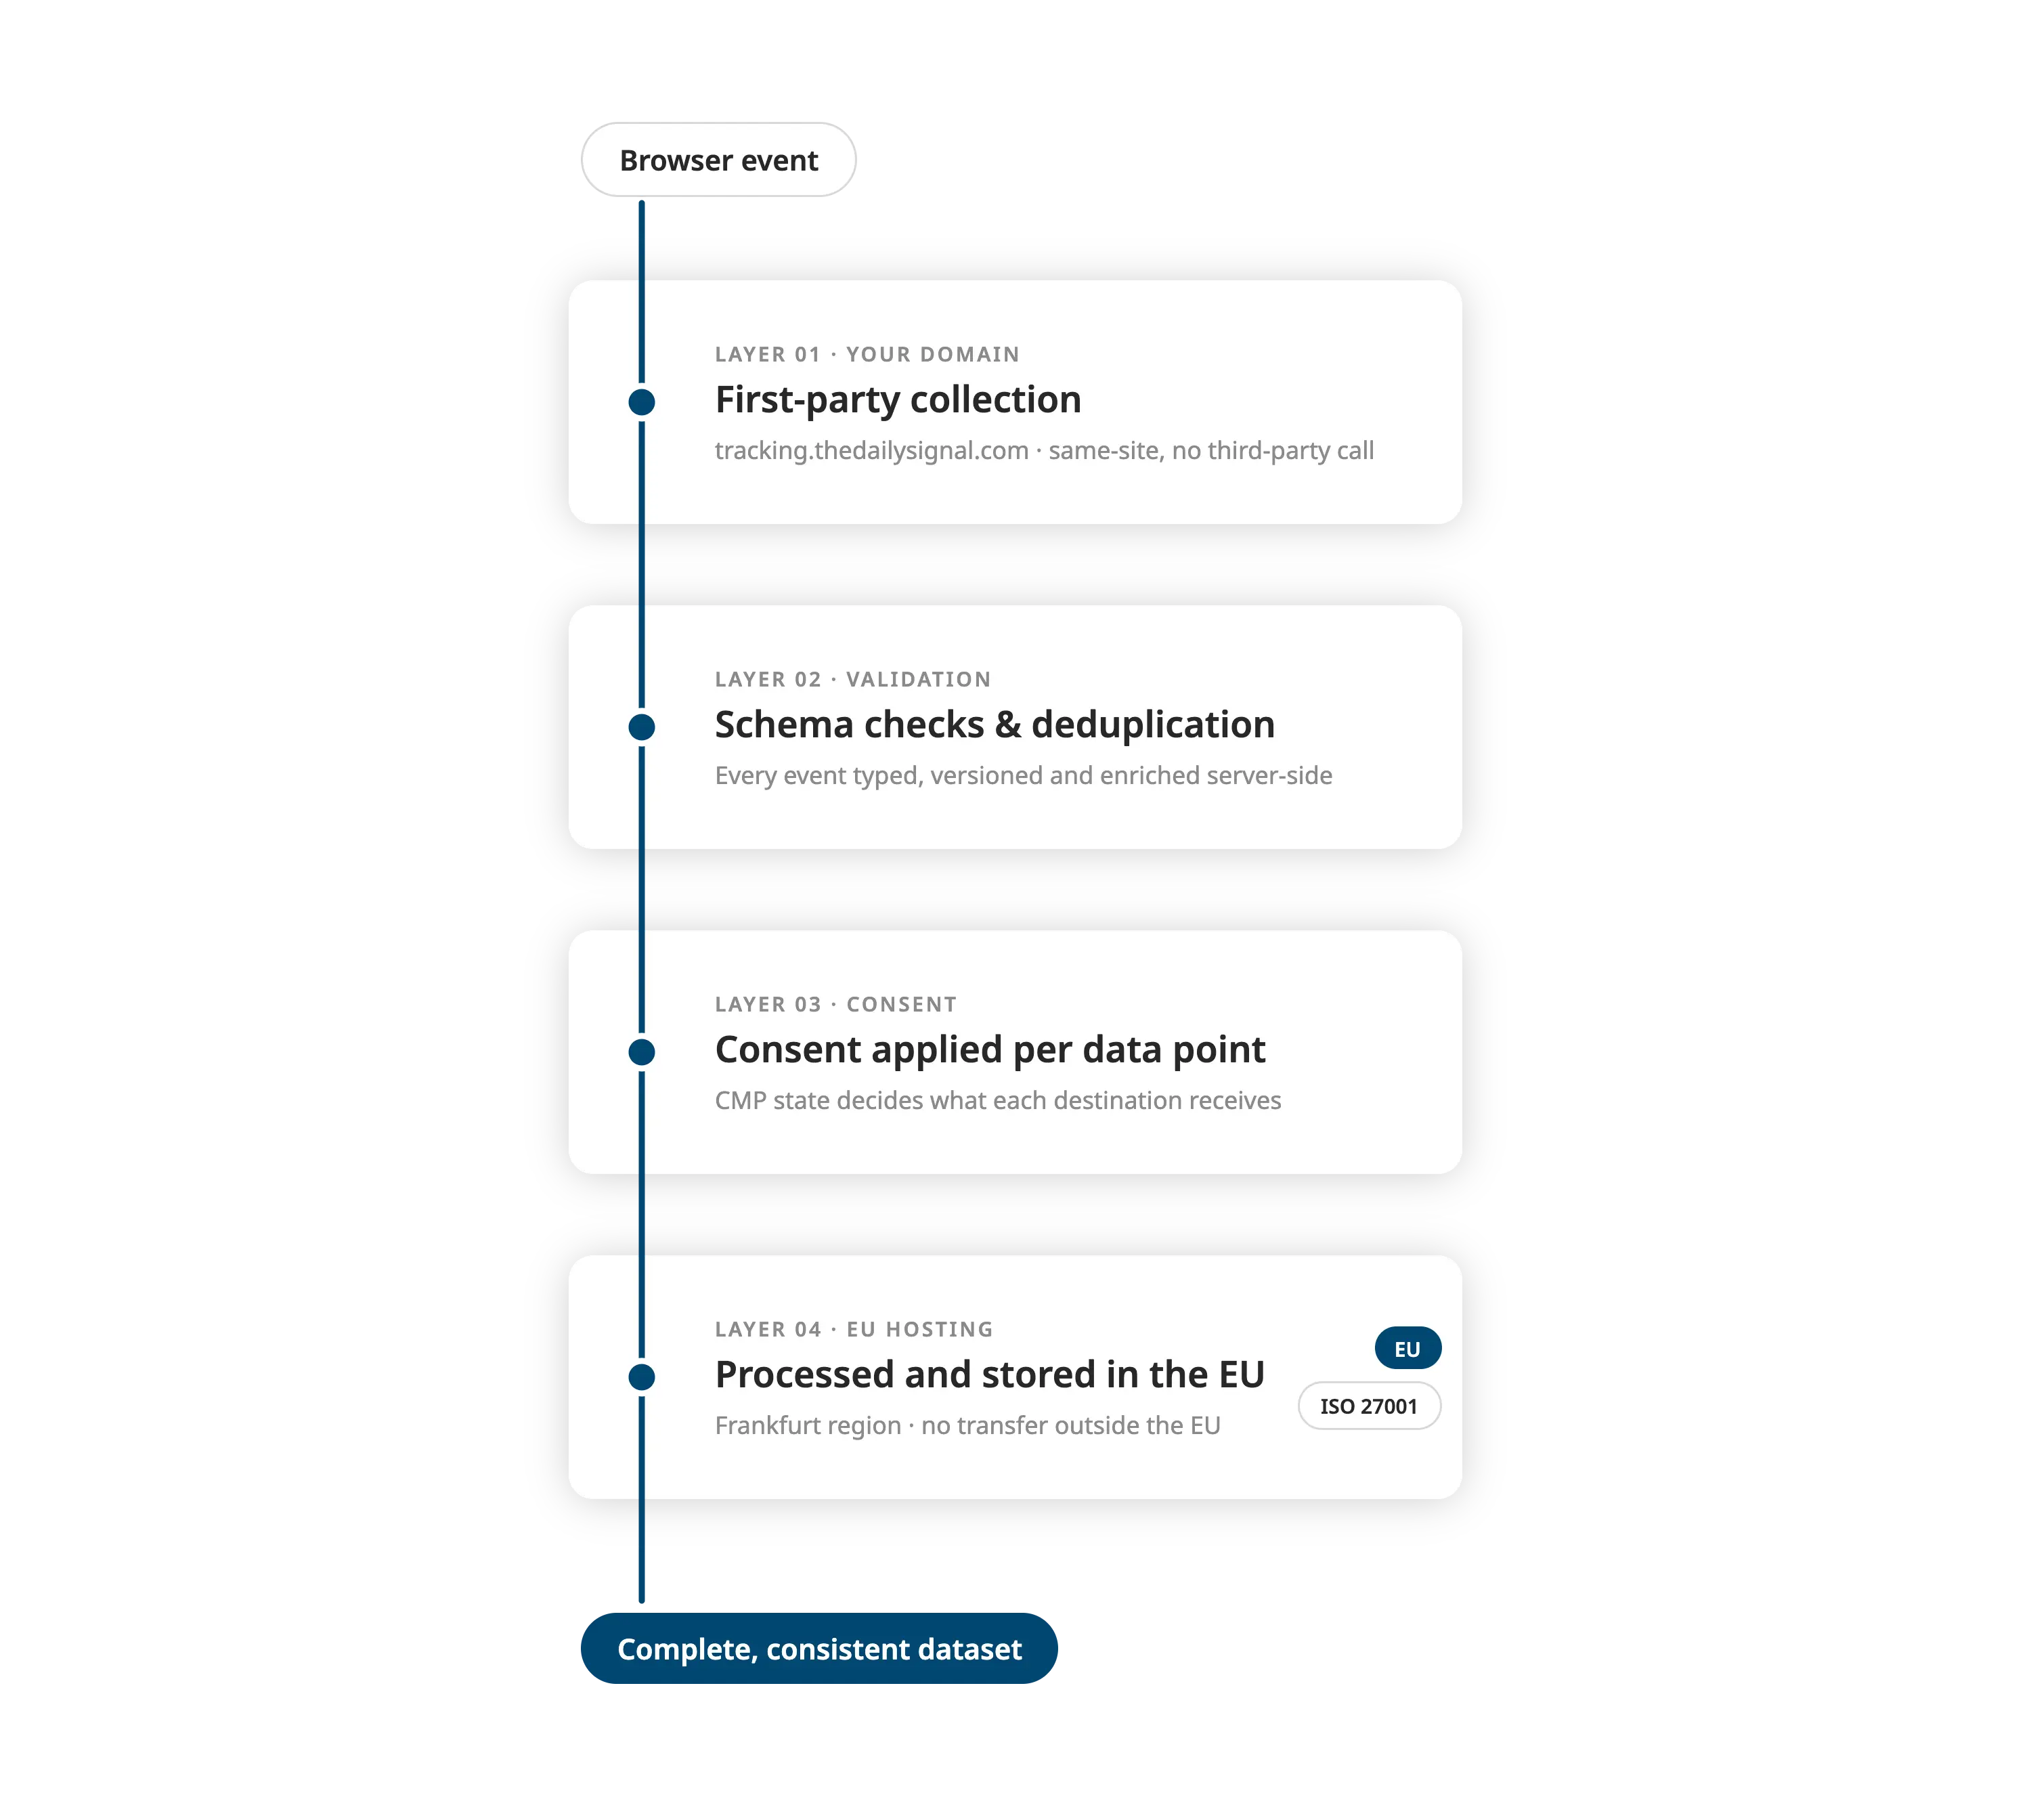
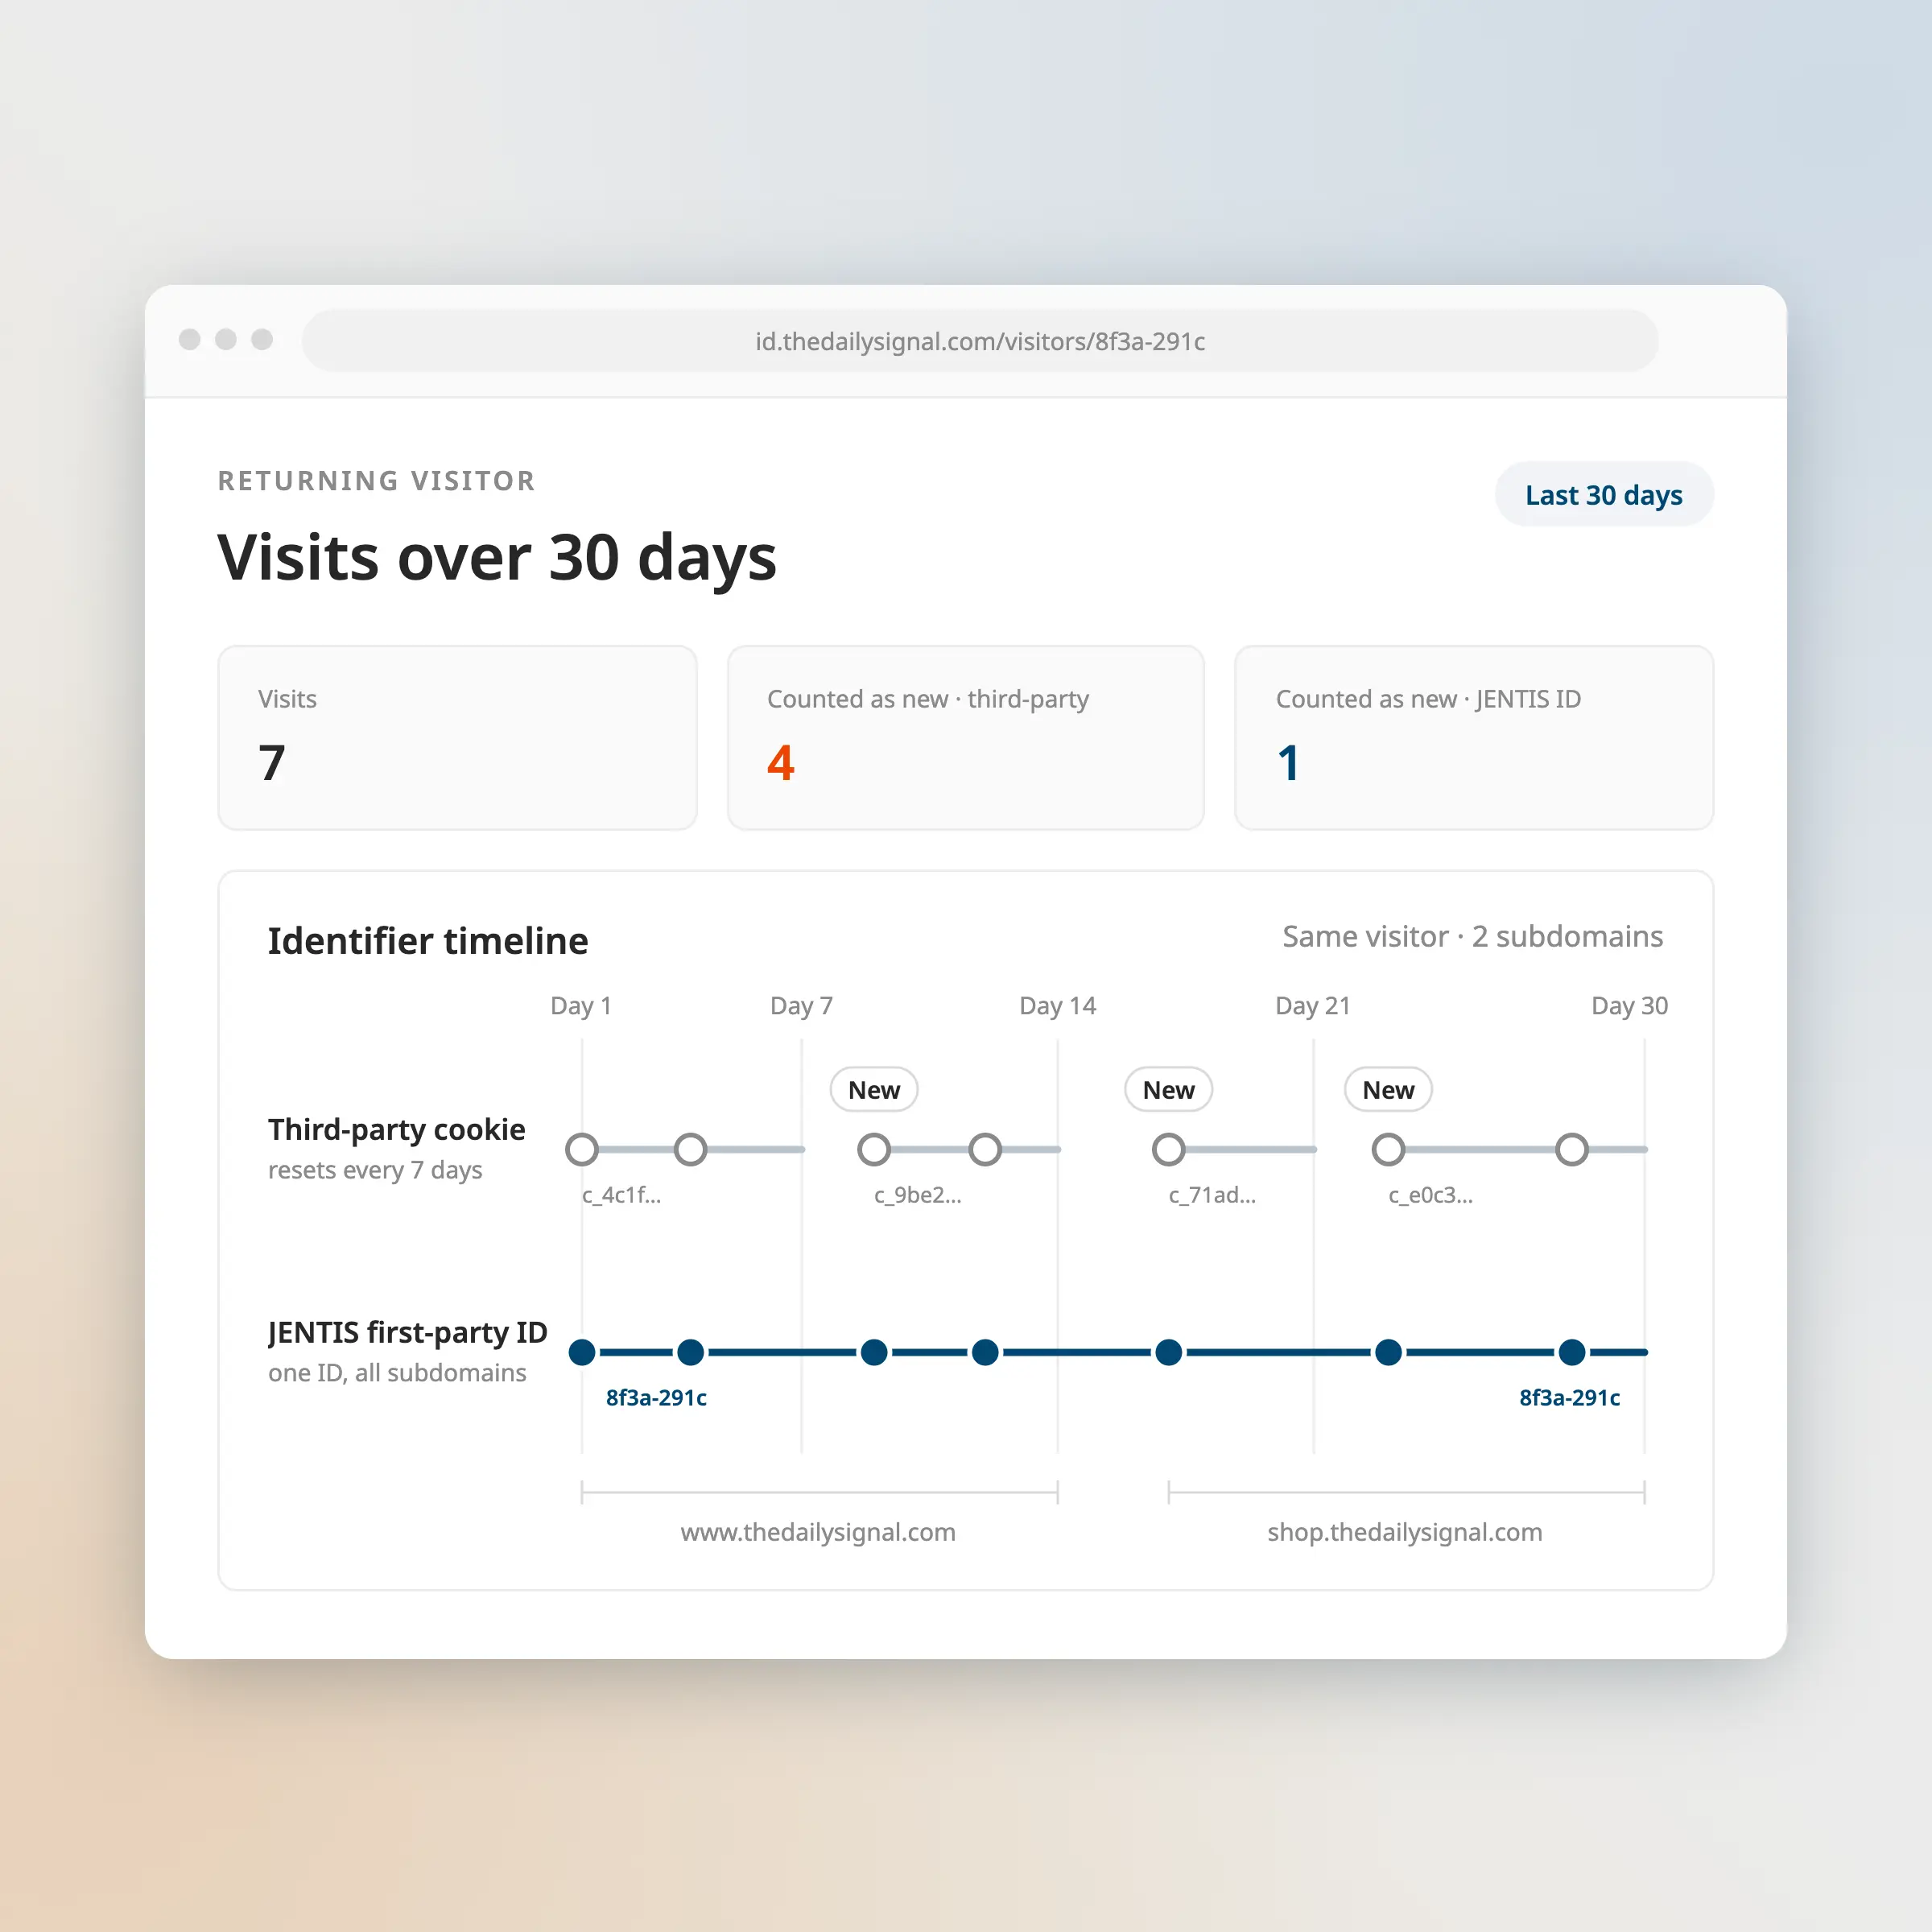
A first-party identifier set from your own domain keeps identity stable across sessions and subdomains. Cookie lifetime is no longer capped by the browser.
- Stable identity: Returning users recognized past Safari's seven-day limit.
- Corrected journeys: Visitors falsely counted as new are attributed correctly.
- Cross-subdomain continuity: One identifier across every property you operate.
Essential Mode
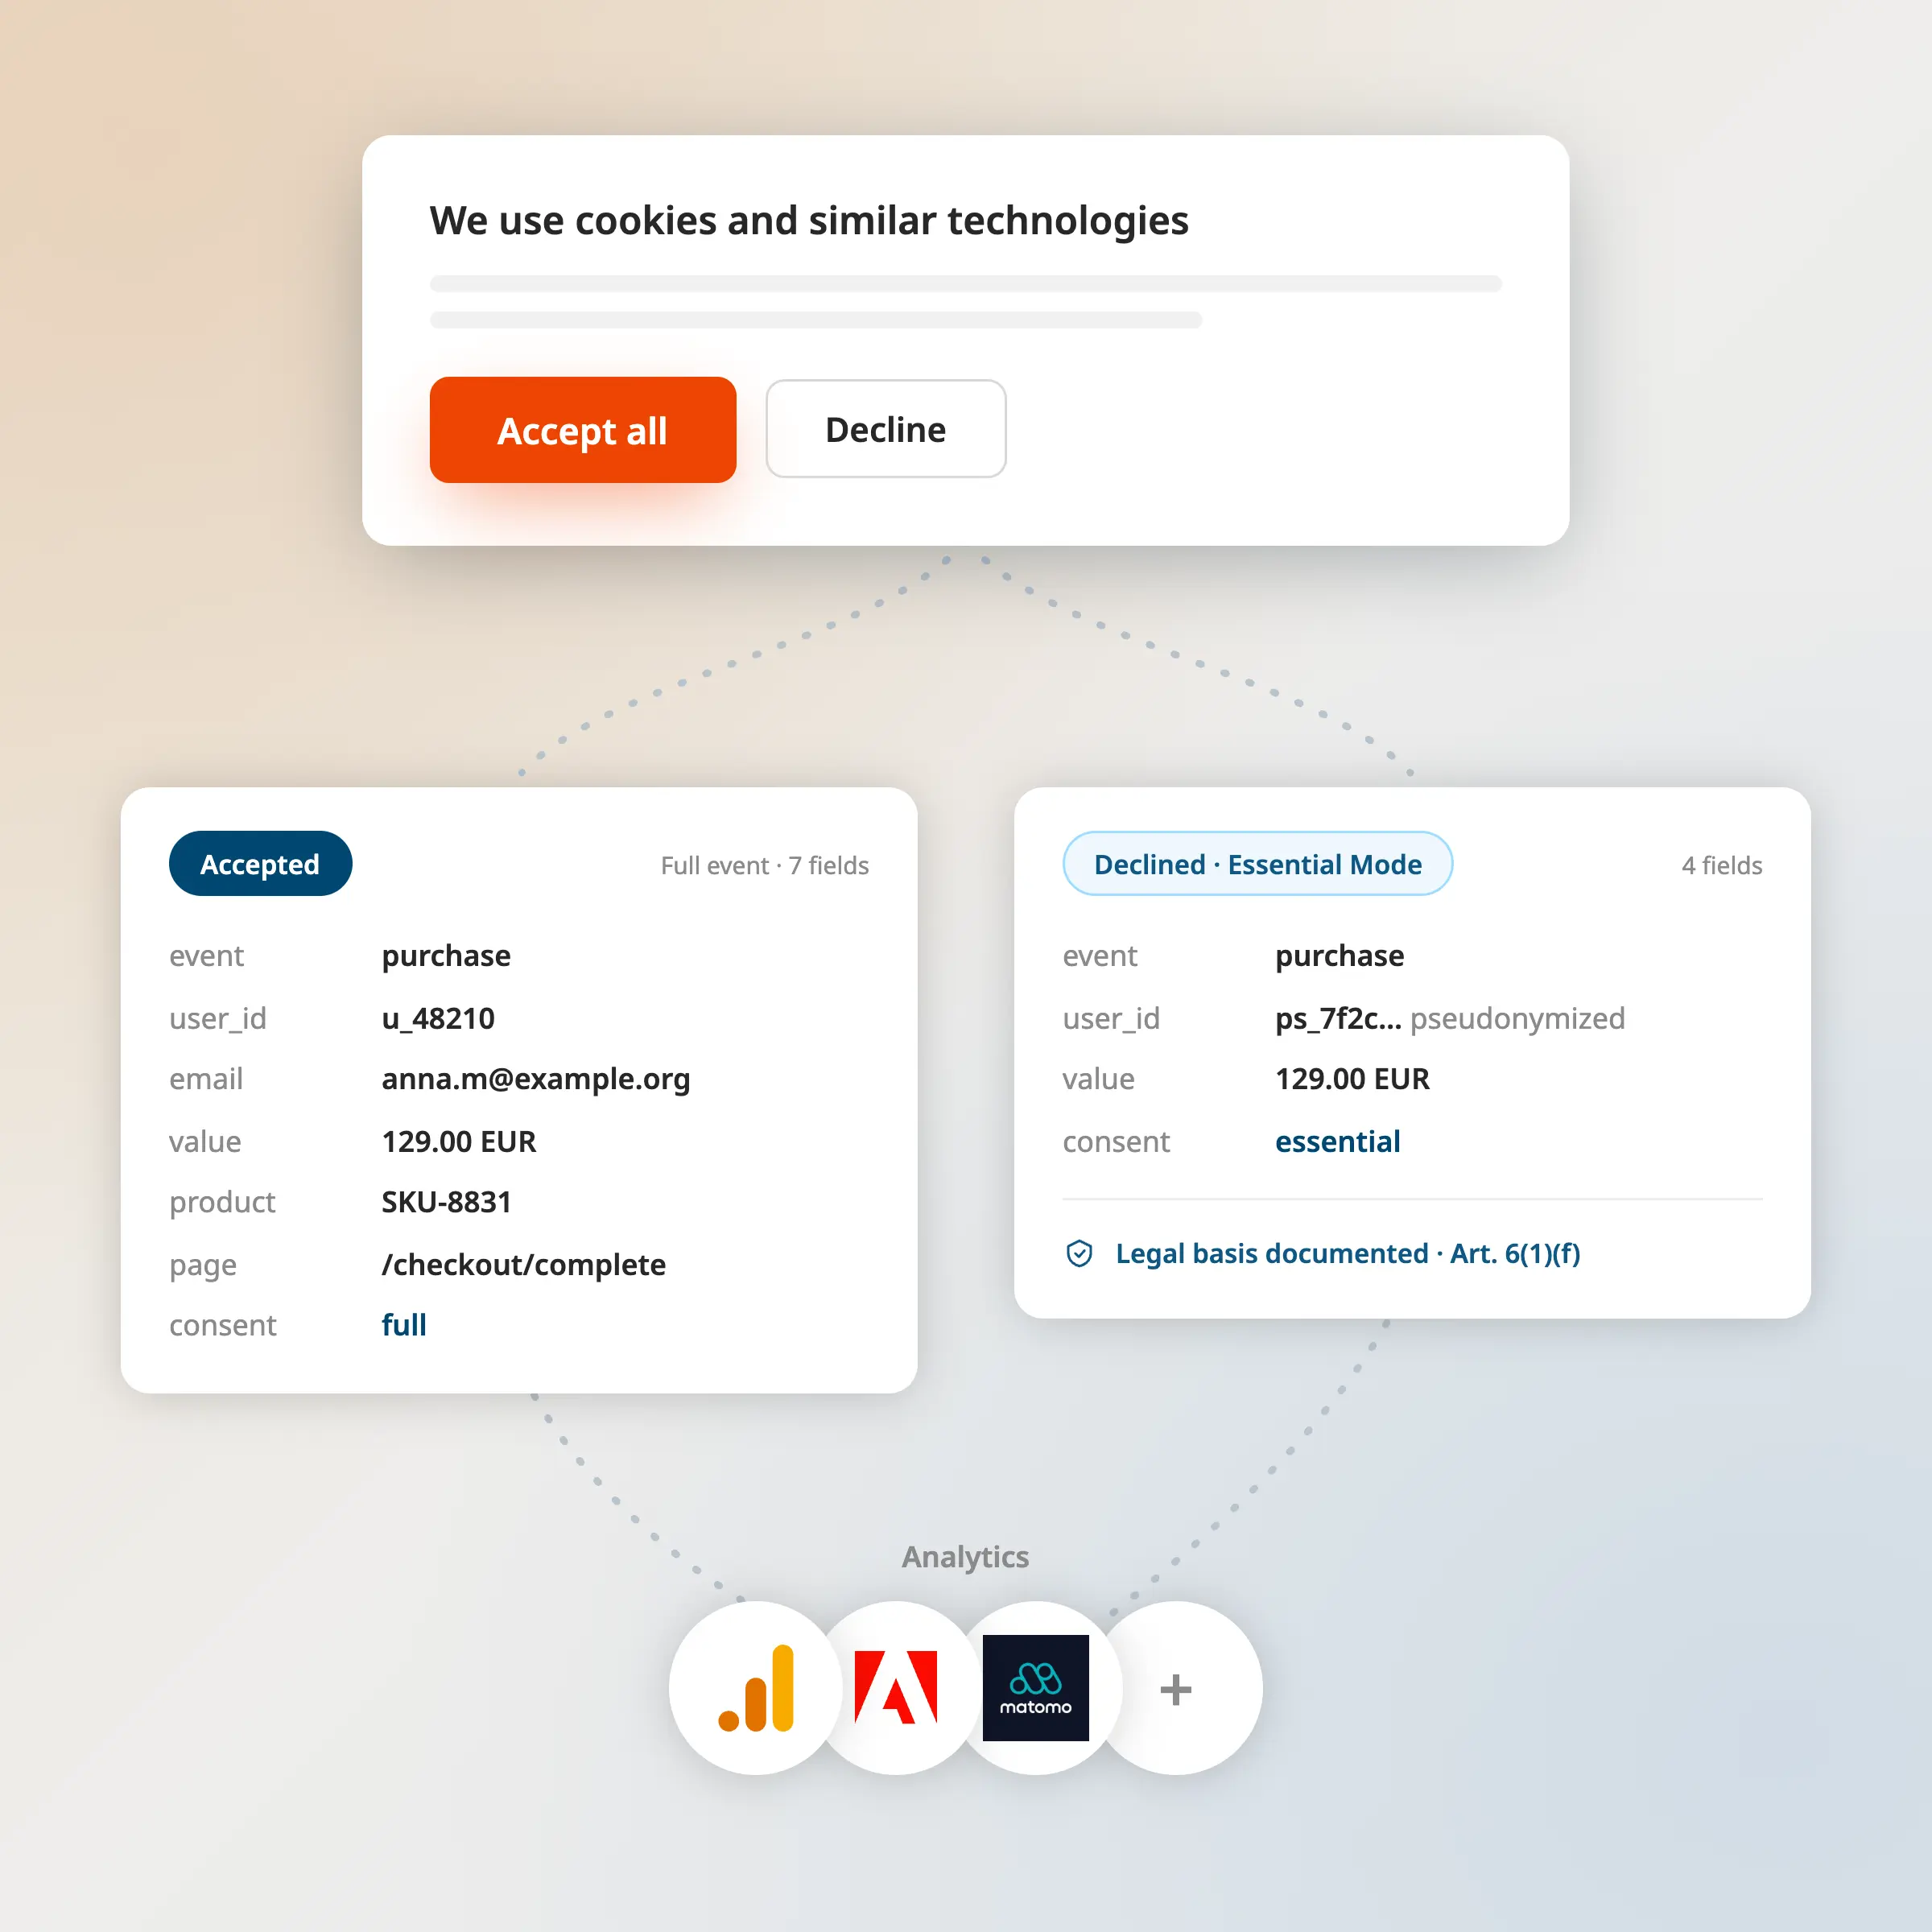
Measure the traffic that denies consent.
When consent is denied, a server-side fallback captures strictly necessary, pseudonymized signals and forwards them to the tools you define.
- Pseudonymized capture: No personal data reaches downstream tools.
- Up to 70% less data loss: Up to 3x more data delivered to analytics tools.
- Legally documented: A defined legal basis your DPO can review.
Synthetic Users
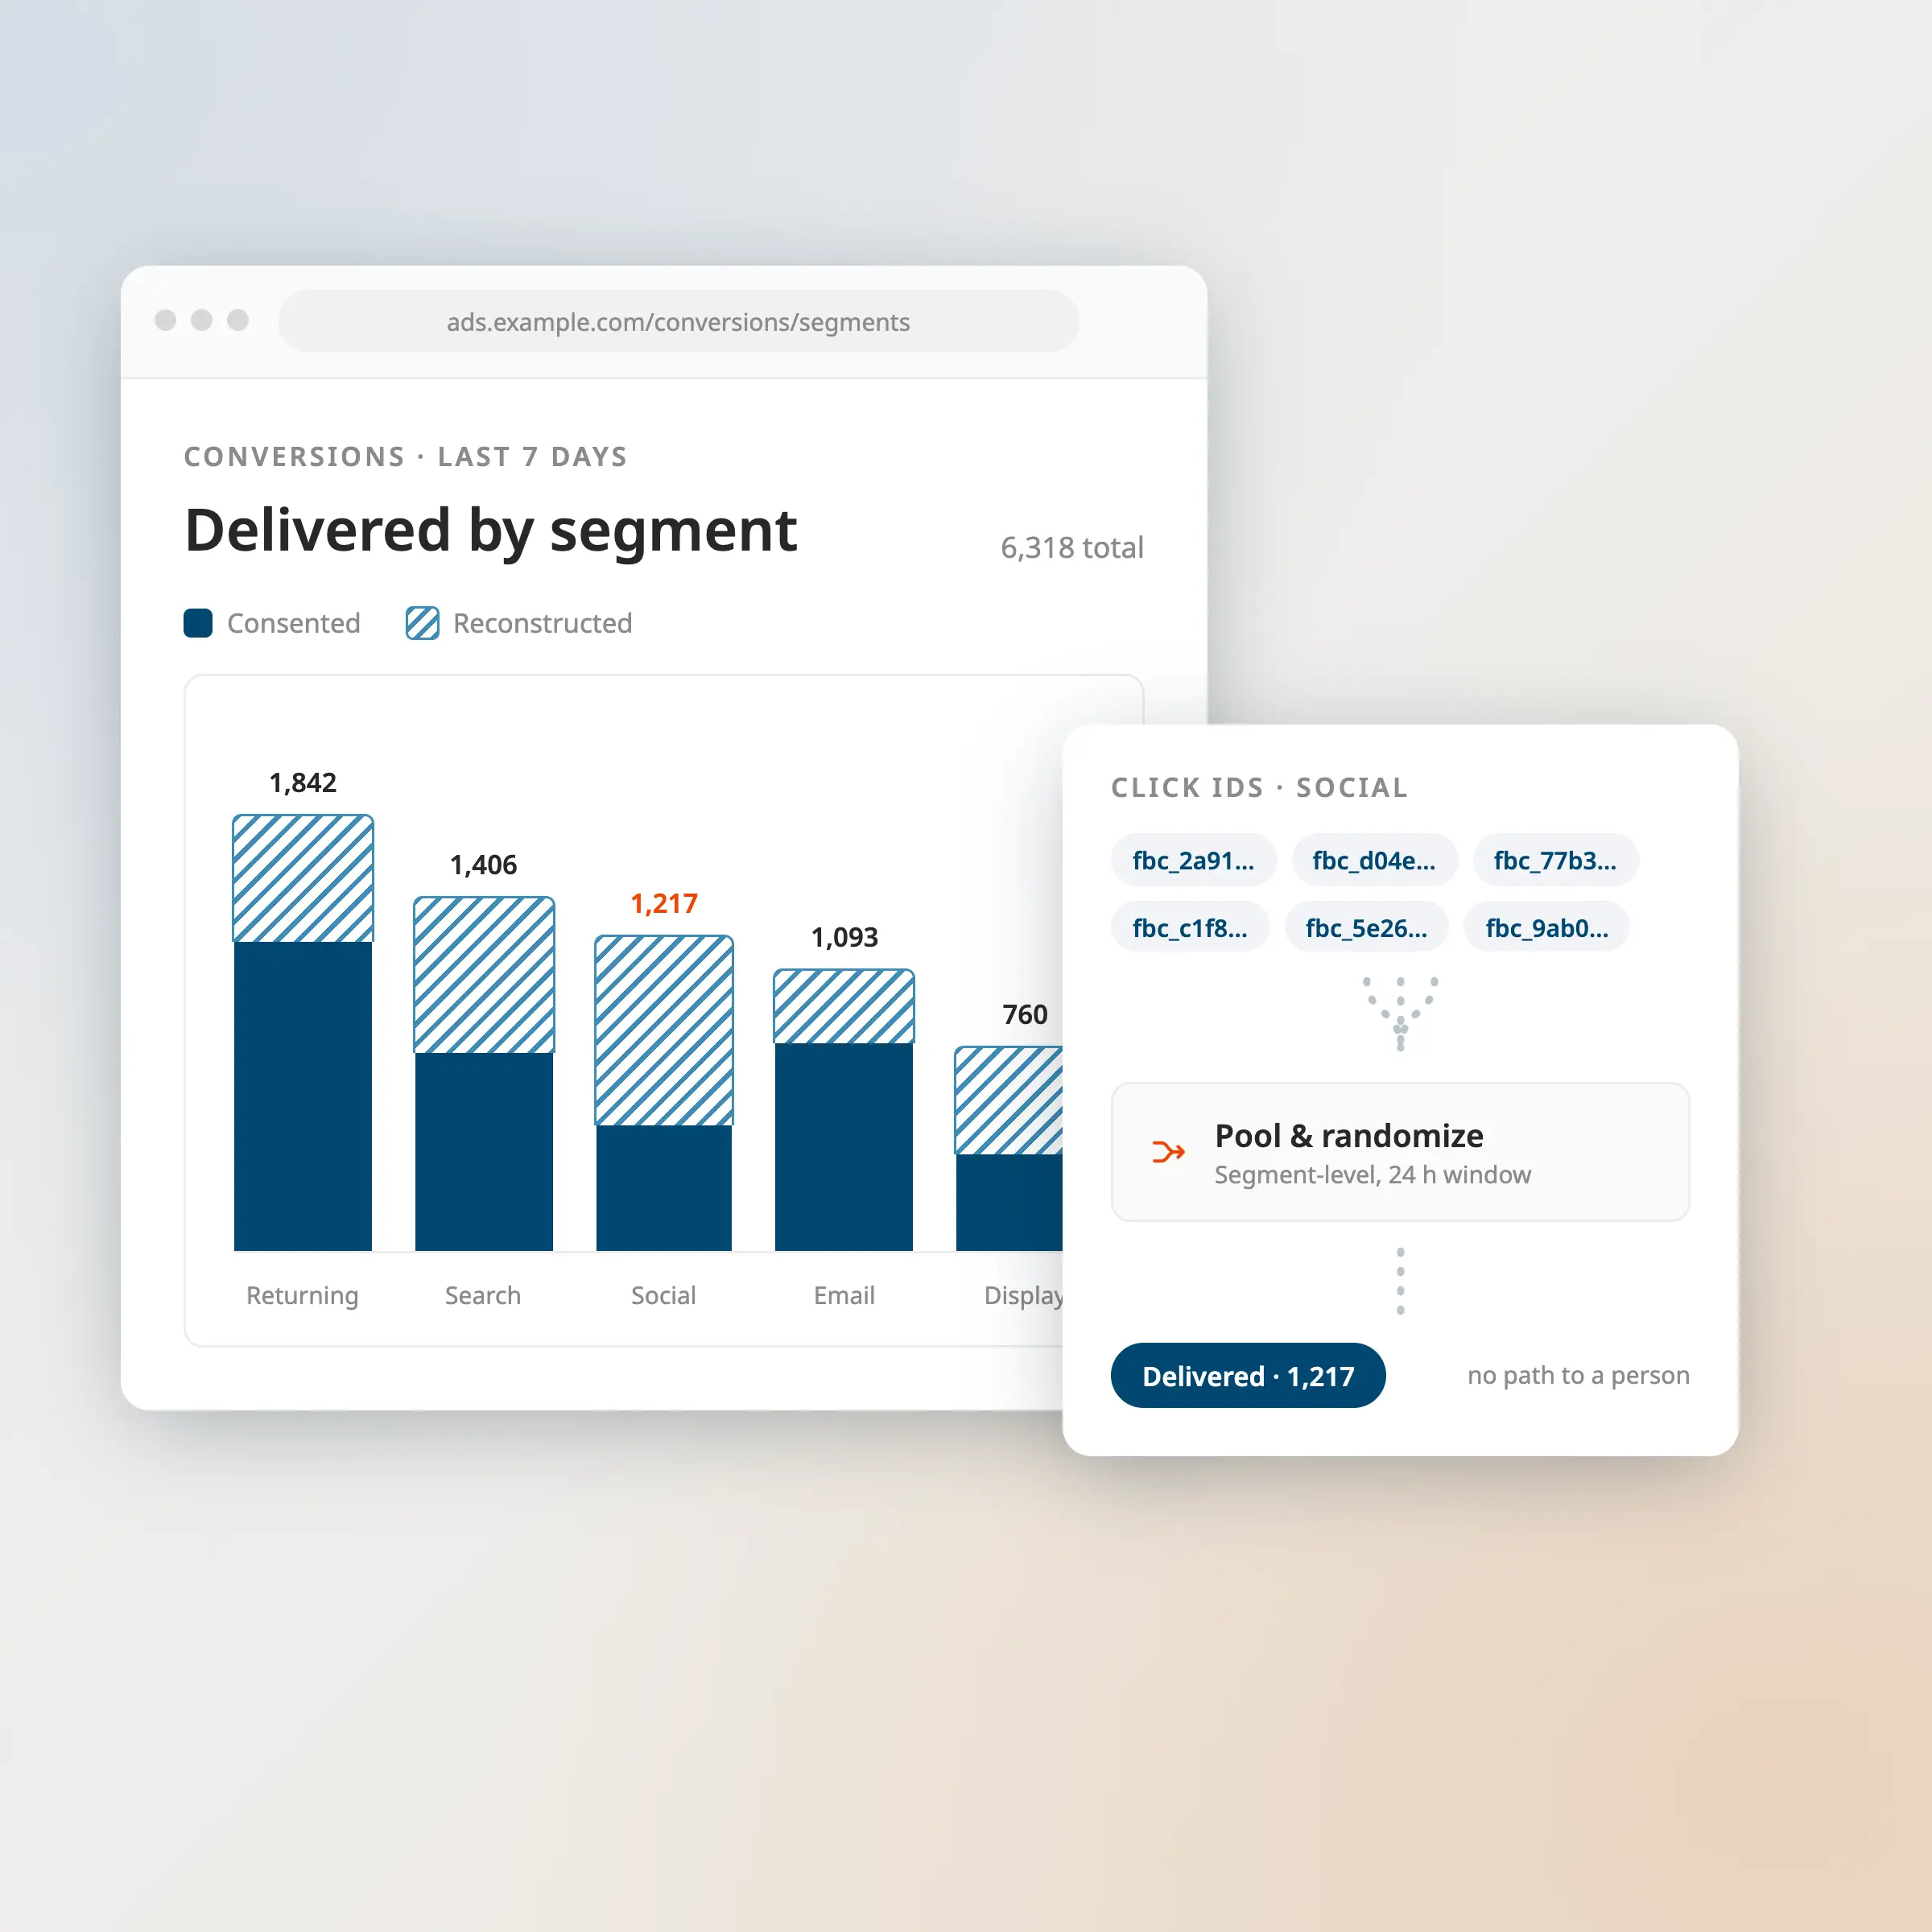
Give ad platforms the conversion signals they are missing.
Models trained on your consented first-party data reconstruct conversion signals for non-consenting visitors. Click IDs are pooled and randomized per segment before delivery, so no ID traces back to an individual.
- Full activation: Google Ads, Meta, and other platforms receive complete conversion signals.
- Grounded in your data: Built on real first-party behavior, not third-party estimation.
- Auditable: Mathematical operations on your own data, under your control.
Native connectors & Privacy Controls
Capture once, forward to 150 destinations.
Native connectors to analytics, advertising, and warehouse destinations, built and maintained by JENTIS as part of the service. Privacy rules are applied server-side before each forward.
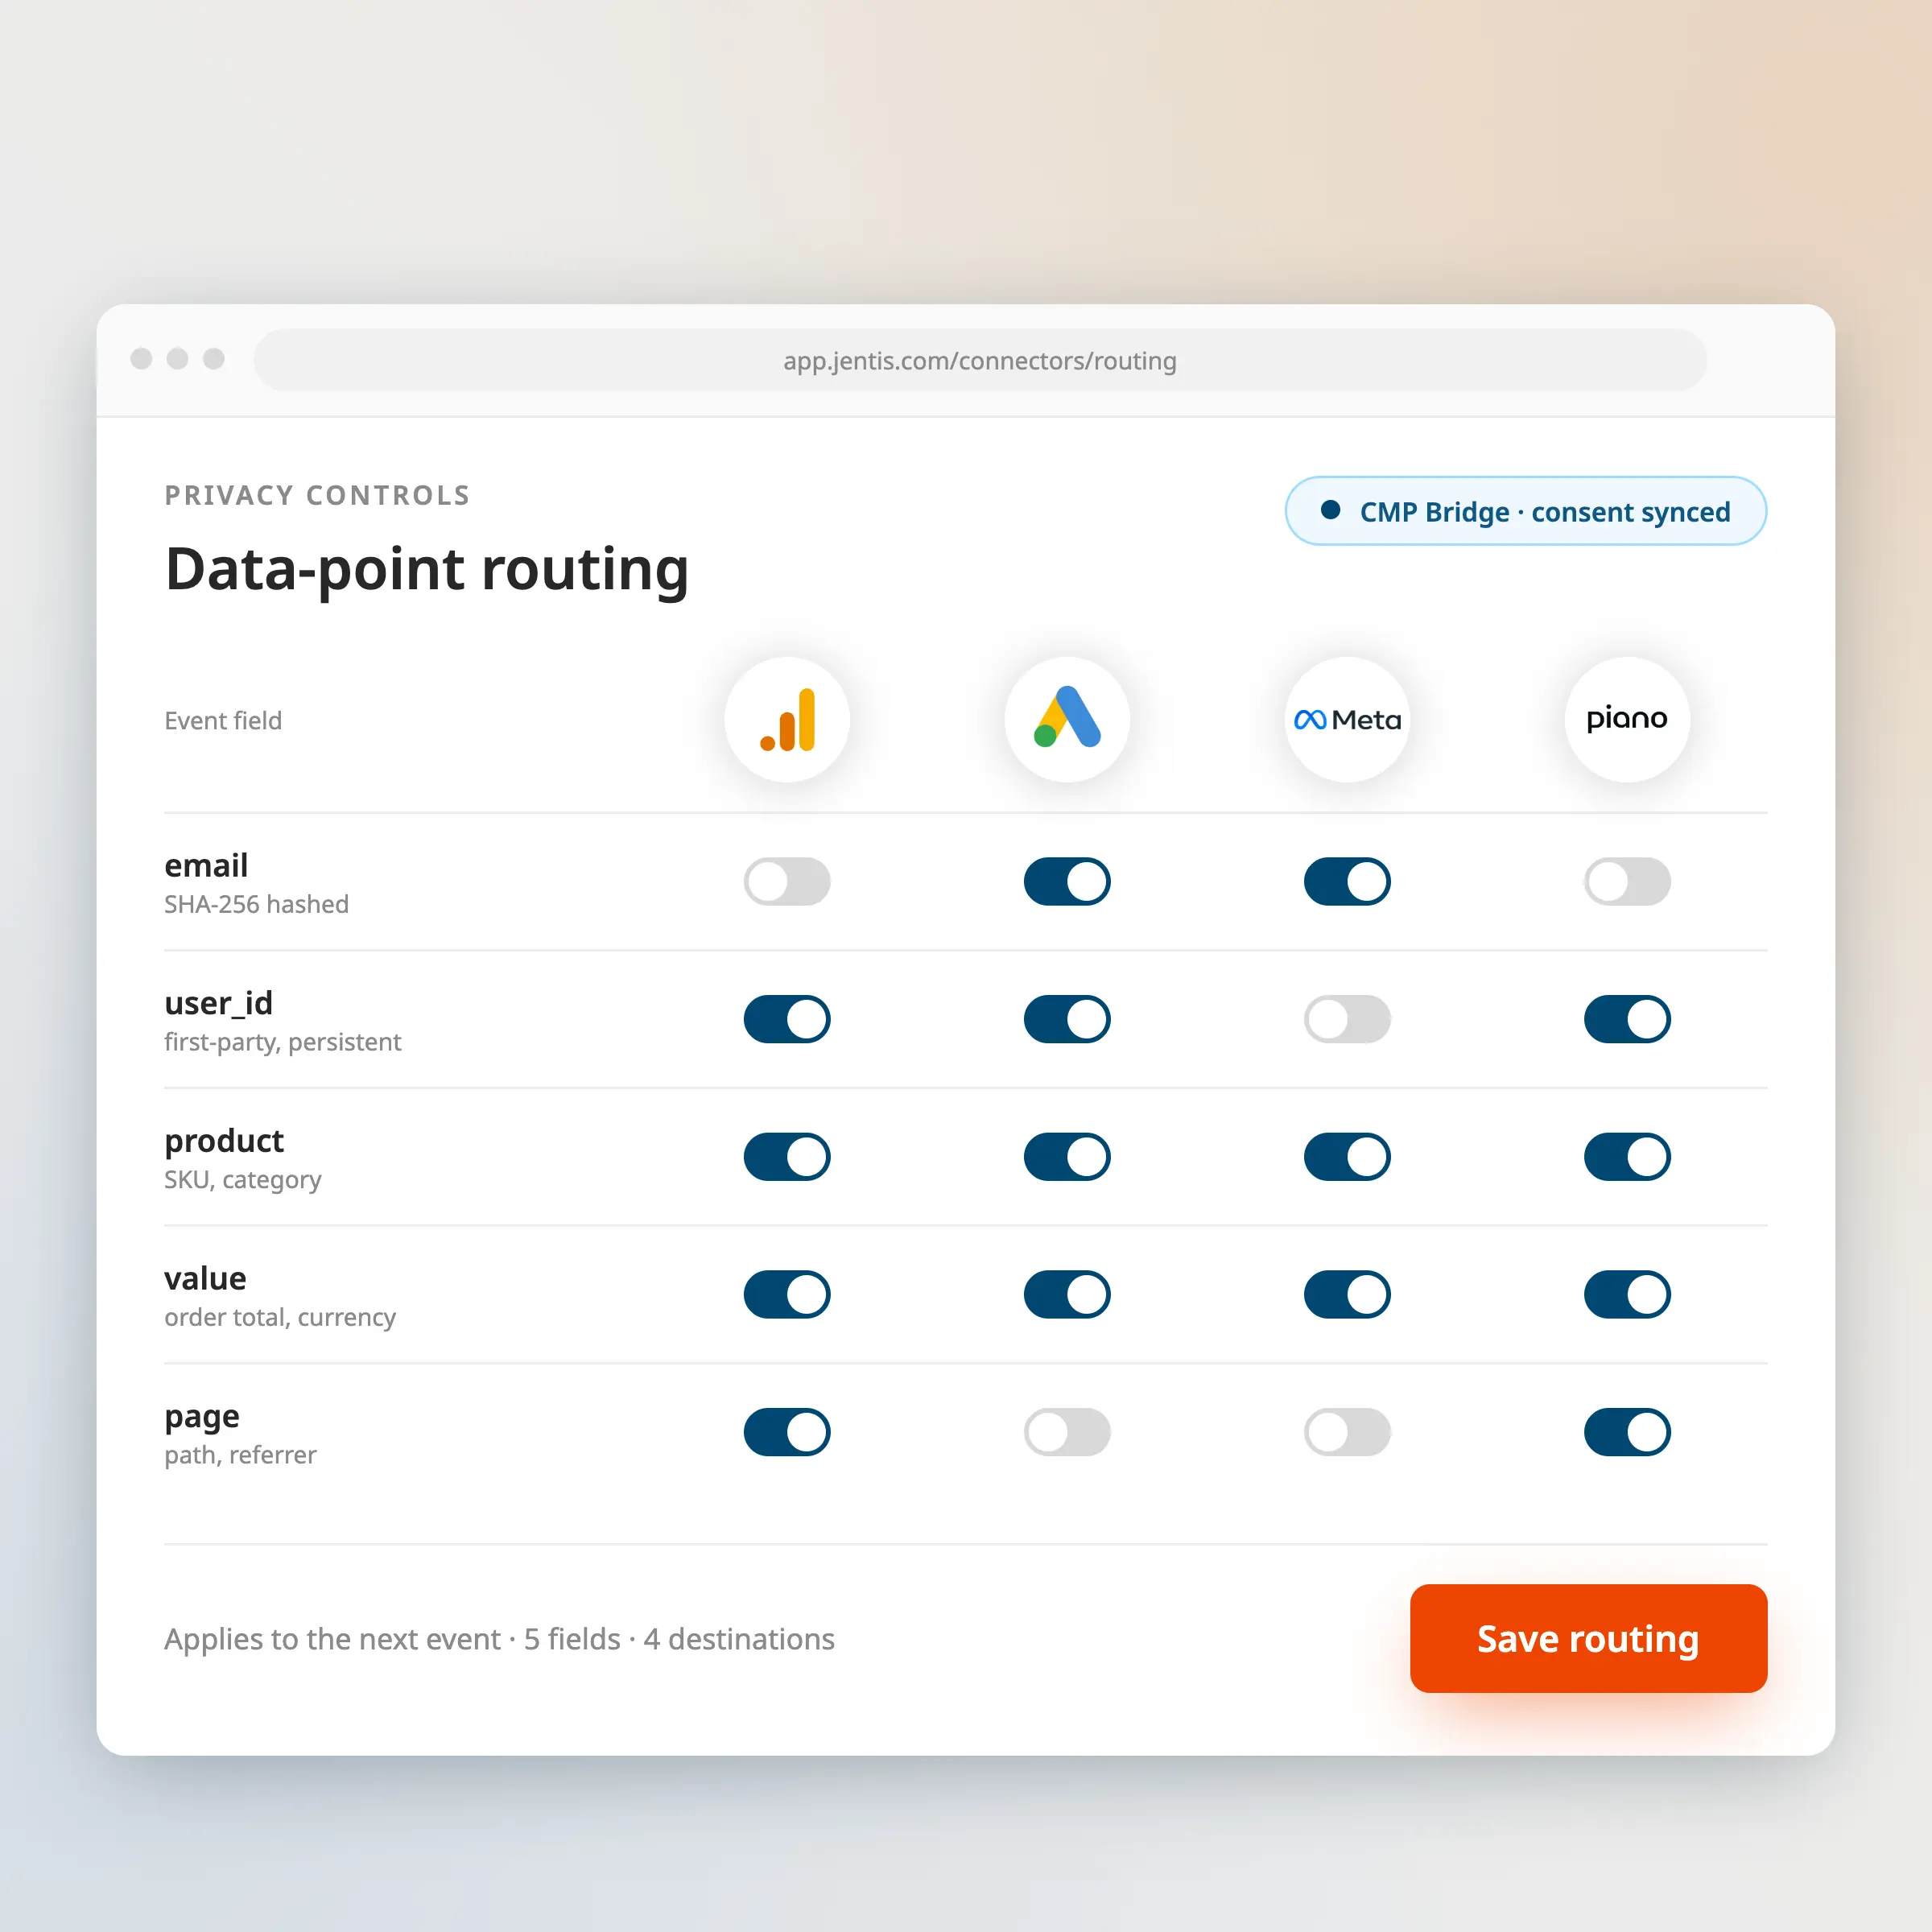
- Data-point-level control: Define exactly which fields reach which vendor.
- CMP Bridge: Auto-syncs consent preferences with tracking. Installs in minutes.
- Maintained for you: Connector updates are part of the service, not an engineering ticket.